
DevSecOps · Software supply chain · FreelanceN 51.22° · E 6.77° — Düsseldorf
DevSecOps.No bullshit.
Consulting, training and software development for German mid-market companies — for 23 years. I take software supply-chain attacks apart in public, before they reach your stack.
Linux Kernel CVE-2026-98432: Two Sockets Share IP Options, and One Frees Them Too EarlyTraefik CVE-2026-114640: The plaintext router passes forged client certificates to the backendLiteLLM 1.107.0: One Line of Build Configuration Turns Every Python Start into a Credential ThiefGo CVE-2026-111943: Why Protection Against the eMudhra Keys Lives in the Binary, Not the Trust StorePHP CVE-2026-109618 and CVE-2026-109619 (PHP2Shell): The Out-of-Memory Escape Hatch Corrupts the InterpreterGitLab CVE-2026-110264: An Org File Overflows Ruby's Regex CompilereMudhra CA compromise (CVE-2026-111943): Eight intermediate certificates with keys you can countNode.js CVE-2026-111497: The Brotli Decoder Keeps Going After an Invalid Block SwitchLinux kernel CVE-2026-80521: The AF_UNIX garbage collector frees a socket it still keeps on its listLinux kernel CVE-2026-99999: A deferred checksum overwrites the already validated IPv4 headerKEDA CVE-2026-77524: The operator sends its own token to foreign Vault serversArgo CD CVE-2026-77459: Delete Hooks Bypass the Boundaries of the AppProject
What I do for you.
01–03Taken apart before it hits you.
Threat-Feed31.10.2026→27.10.2026→26.10.2026→22.10.2026→
Linux Kernel CVE-2026-98432: Two Sockets Share IP Options, and One Frees Them Too Early
CVE-2026-98432 · CVSS 9.8 · Linux kernel 4.4 and later before 5.10.272 / 5.15.223 / 6.1.190 / 6.6.159 / 6.12.113 / 6.18.56 / 7.2.10 · Fix e3f33b0a1d89
Traefik CVE-2026-114640: The plaintext router passes forged client certificates to the backend
CVE-2026-114640 · CVSS 8.7 · Traefik 3.7.0 to 3.7.13 · Fix 3.7.14
LiteLLM 1.107.0: One Line of Build Configuration Turns Every Python Start into a Credential Thief
No CVE · supply-chain compromise · litellm 1.107.0 (PyPI, Docker Hub, GHCR) · clean: 1.106.2
Go CVE-2026-111943: Why Protection Against the eMudhra Keys Lives in the Binary, Not the Trust Store
CVE-2026-111943 (GO-2026-6809) · CVSS 6.8 (Amazon) · Go before 1.26.10 and 1.27.0 to 1.27.2 · Fix 1.26.10 / 1.27.3
Who's behind this
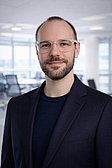
Kai Ole Hartwig
Freelance DevSecOps consultant · OnlyOle Consulting
Programming since 2002 – self-taught, set up my own business with KO-Web in 2012. Over 100 projects, with a focus on security, performance, automation and quality. Today freelance: DevSecOps consulting, training and software development.
ContactSounds like a fit?
Book a call
Sounds like a fit?
Then write to me.
No form marathon, no sales funnel. A short message — I get back to you personally and tell you honestly whether I can help.